Compare commits
| Author | SHA1 | Date | |
|---|---|---|---|
 PYDT |
08bdd870a5 | ||
|
PYDT
|
54a43f6045 | ||
|
PYDT
|
25a9cc3608 | ||
|
PYDT
|
7f52a53e62 | ||
|
PYDT
|
20e9c82854 | ||
|
PYDT
|
fe92e53f7b | ||
|
PYDT
|
130aeb01b9 | ||
|
PYDT
|
7439b5e362 | ||
|
PYDT
|
166059b9bd | ||
|
PYDT
|
7e5fc40768 | ||
|
PYDT
|
aadb2c1e40 | ||
|
PYDT
|
f317452c80 | ||
|
PYDT
|
cb98a00cfa | ||
|
PYDT
|
75deeb247a | ||
|
PYDT
|
b17eec0647 | ||
|
PYDT
|
5ddcc24563 | ||
|
PYDT
|
9b4ecdf7bf | ||
|
PYDT
|
6ba4efe1bb | ||
|
PYDT
|
84ae6b4247 | ||
|
PYDT
|
7510c6a539 | ||
|
PYDT
|
de45907c91 | ||
|
PYDT
|
17e9546671 |
No files matched your search
@@ -1 +0,0 @@
|
||||
0
|
||||

Binary file not shown.
|
Before Width: | Height: | Size: 16 KiB |
@@ -0,0 +1 @@
|
||||
function_list = ['_CorExeMain', ['LoadLibraryA', 'OpenMutexW', 'SetLocaleInfoA', 'FindNextVolumeA', 'GetNamedPipeHandleStateA', 'FileTimeToLocalFileTime', 'EnumResourceTypesA', 'EnumResourceNamesA', 'FillConsoleOutputCharacterA', 'DeleteTimerQueueTimer', 'TerminateThread', 'SetLastError', 'GetVersionExA', 'FreeResource', 'SetEvent', 'FindNextFileW', 'CopyFileExA', 'BuildCommDCBA', 'ReadConsoleOutputCharacterW', 'SetDefaultCommConfigW', 'VerLanguageNameW', 'GetCommConfig', 'WritePrivateProfileStructA', 'LocalFree', 'FindNextVolumeMountPointA', 'ReadConsoleInputA', 'WriteConsoleInputW', 'LoadResource', 'AddAtomA', 'GlobalDeleteAtom', 'GetThreadPriority', 'CallNamedPipeA', 'GetDriveTypeW', 'BuildCommDCBAndTimeoutsW', 'GetProcAddress', 'GlobalAlloc', 'GlobalFix', 'FindFirstChangeNotificationA', 'VerifyVersionInfoA', 'FormatMessageA', 'SetDllDirectoryA', 'GetModuleHandleA', 'WritePrivateProfileStringW', 'GetUserDefaultLCID', 'SetDllDirectoryW', 'SetConsoleTextAttribute', 'InterlockedDecrement', 'GetStartupInfoA', 'GetSystemWow64DirectoryW', 'CopyFileA', 'SetCalendarInfoW', 'DebugBreak', 'SetConsoleCursorInfo', 'FreeLibraryAndExitThread', 'GetModuleFileNameW', 'GetConsoleAliasExesLengthW', 'WaitForDebugEvent', 'InterlockedExchangeAdd', 'CopyFileW', 'GetOEMCP', 'GetPrivateProfileStringA', 'CreateActCtxA', 'ReadConsoleInputW', 'OutputDebugStringA', 'PulseEvent', 'SetThreadAffinityMask', 'FlushConsoleInputBuffer', 'lstrlenA', 'WriteConsoleW', 'lstrcpyA', 'UnlockFile', 'FreeEnvironmentStringsA', 'GetConsoleCP', 'CreateIoCompletionPort', 'FreeConsole', 'GlobalGetAtomNameW', 'SetComputerNameA', 'GetConsoleAliasExesLengthA', 'CreateMailslotW', 'SetCommState', 'MoveFileWithProgressW', 'GetSystemTimeAdjustment', 'EnumSystemLocalesW', 'GetPrivateProfileIntA', 'WriteProfileStringW', 'GetLastError', 'OpenWaitableTimerW', 'GetConsoleAliasesLengthA', 'PeekNamedPipe', 'FillConsoleOutputCharacterW', 'BuildCommDCBAndTimeoutsA', 'GetConsoleAliasExesA', 'InterlockedIncrement', 'Sleep', 'InitializeCriticalSection', 'DeleteCriticalSection', 'EnterCriticalSection', 'LeaveCriticalSection', 'RaiseException', 'TerminateProcess', 'GetCurrentProcess', 'UnhandledExceptionFilter', 'SetUnhandledExceptionFilter', 'IsDebuggerPresent', 'RtlUnwind', 'GetModuleHandleW', 'ExitProcess', 'DeleteFileA', 'GetStartupInfoW', 'HeapValidate', 'IsBadReadPtr', 'TlsGetValue', 'TlsAlloc', 'TlsSetValue', 'GetCurrentThreadId', 'TlsFree', 'GetStdHandle', 'WriteFile', 'GetFileType', 'OutputDebugStringW', 'LoadLibraryW', 'GetModuleFileNameA', 'GetACP', 'GetCPInfo', 'IsValidCodePage', 'InitializeCriticalSectionAndSpinCount', 'SetHandleCount', 'QueryPerformanceCounter', 'GetTickCount', 'GetCurrentProcessId', 'GetSystemTimeAsFileTime', 'FreeEnvironmentStringsW', 'GetEnvironmentStringsW', 'GetCommandLineW', 'HeapDestroy', 'HeapCreate', 'HeapFree', 'VirtualFree', 'FlushFileBuffers', 'WideCharToMultiByte', 'GetConsoleMode', 'HeapAlloc', 'HeapSize', 'HeapReAlloc', 'VirtualAlloc', 'MultiByteToWideChar', 'LCMapStringA', 'LCMapStringW', 'GetStringTypeA', 'GetStringTypeW', 'GetLocaleInfoA', 'SetFilePointer', 'SetStdHandle', 'WriteConsoleA', 'GetConsoleOutputCP', 'CloseHandle', 'CreateFileA'], ['SetErrorMode', 'LoadLibraryW', 'FlushFileBuffers', 'CloseHandle', 'CreateFileW', 'IsProcessorFeaturePresent', 'HeapReAlloc', 'GetStringTypeW', 'LCMapStringW', 'WriteConsoleW', 'SetStdHandle', 'GetSystemTimeAsFileTime', 'HeapAlloc', 'GetLastError', 'HeapFree', 'GetCommandLineW', 'HeapSetInformation', 'GetStartupInfoW', 'TerminateProcess', 'GetCurrentProcess', 'UnhandledExceptionFilter', 'SetUnhandledExceptionFilter', 'IsDebuggerPresent', 'GetProcAddress', 'GetModuleHandleW', 'ExitProcess', 'DecodePointer', 'WriteFile', 'GetStdHandle', 'GetModuleFileNameW', 'HeapCreate', 'EncodePointer', 'RaiseException', 'TlsAlloc', 'TlsGetValue', 'TlsSetValue', 'TlsFree', 'InterlockedIncrement', 'SetLastError', 'GetCurrentThreadId', 'InterlockedDecrement', 'FreeEnvironmentStringsW', 'GetEnvironmentStringsW', 'SetHandleCount', 'InitializeCriticalSectionAndSpinCount', 'GetFileType', 'DeleteCriticalSection', 'QueryPerformanceCounter', 'GetTickCount', 'GetCurrentProcessId', 'LeaveCriticalSection', 'EnterCriticalSection', 'SetFilePointer', 'WideCharToMultiByte', 'GetConsoleCP', 'GetConsoleMode', 'GetCPInfo', 'GetACP', 'GetOEMCP', 'IsValidCodePage', 'Sleep', 'MultiByteToWideChar', 'HeapSize', 'RtlUnwind', 'PostQuitMessage', 'DefWindowProcW', 'DestroyWindow', 'UpdateWindow', 'CreateWindowExW', 'RegisterClassExW', 'DispatchMessageW', 'TranslateMessage', 'TranslateAcceleratorW', 'GetMessageW', 'LoadAcceleratorsW'], ['htonl', 'FindClose', 'FindFirstFileA', 'GetVolumeInformationA', 'WaitForSingleObject', 'CreateMutexA', 'OpenMutexA', 'ReadFile', 'FindNextFileA', 'FreeLibrary', 'GetTempPathA', 'GetSystemDirectoryA', 'GetSystemTime', 'lstrlenA', 'lstrcpynA', 'GetComputerNameA', 'OpenProcess', 'GetVersionExA', 'GetModuleFileNameA', 'LocalFree', 'LocalAlloc', 'GetCurrentProcess', 'GetCurrentThread', 'CreateMutexW', Line truncated
|
||||
@@ -1,75 +0,0 @@
|
||||
english_list = {"提示":"Tips",
|
||||
"已開啟":"On", "已關閉":"Off",
|
||||
"已开启":"On", "已关闭":"Off",
|
||||
"On":"On", "Off":"Off",
|
||||
"存取被拒":"Access denied",
|
||||
"添加數據庫":"Add database",
|
||||
"個病毒":" Virus",
|
||||
'正在掃描: ':'Scanning: ',
|
||||
"掃描失敗。":"Scan failed.",
|
||||
"病毒掃描":"Virus scan",
|
||||
"正在刪除: ":"Deleting: ",
|
||||
"請選擇掃描方式":"Please select a scan method",
|
||||
"正在初始化中,請稍後...":"Initializing, please wait...",
|
||||
'當前未發現惡意軟體。':'No malware currently found.',
|
||||
"這部裝置已受到保護":"This device has been protected",
|
||||
"這部裝置目前不安全":"This device is currently unsafe",
|
||||
"當前已發現惡意軟體共{}項。":"A total of {} items of malware have been found so far.",
|
||||
"錯誤":"Error", "錯誤: ":"Error: ",
|
||||
"安全密鑰錯誤":"Security Key Error",
|
||||
"尚未啟用實時防護":"Real-time Protect is not enabled",
|
||||
"請輸入需要尋找的檔案":"Please enter the file you want to find",
|
||||
"成功: 已執行成功。":"Success: Executed successfully.",
|
||||
"錯誤: 執行失敗。":"Error: Execution failed.",
|
||||
"完成":'Finish',
|
||||
"您確定要修復系統權限嗎?":"Are you sure you want to fix system permissions?",
|
||||
"修復完成!":"Repair complete!",
|
||||
"您確定要修復系統檔案嗎?":"Are you sure you want to repair the system files?",
|
||||
"修復系統檔案":'Repair System Files',
|
||||
"修復失敗":"Repair failed",
|
||||
'清理系統檔案':'Clean up system files',
|
||||
"您確定要清理系統檔案嗎?":"Are you sure you want to clean the system files?",
|
||||
"清理完成":"Cleanup complete",
|
||||
"清理失敗":"Cleanup failed",
|
||||
"啟用安全模式":"Enable safe mode",
|
||||
"您確定啟用安全模式嗎?":"Are you sure you enable safe mode?",
|
||||
"使用該選項後需要重啟,現在要重啟嗎?":"A reboot is required after using this option, do you want to reboot now?",
|
||||
"啟用失敗":"Enable failed",
|
||||
'禁用安全模式':'Disable safe mode',
|
||||
"您確定禁用安全模式嗎?":"Are you sure you want to disable Safe Mode?",
|
||||
"禁用失敗":"Disable failed",
|
||||
"刪除檔案":"Delete file",
|
||||
"您確定刪除該檔案嗎?":"Are you sure you want to delete this file?",
|
||||
"刪除成功":"Success to deleted",
|
||||
"刪除失敗":"Failed to delete",
|
||||
"運行成功":"Run successfully",
|
||||
"不是有效命令":"Not a valid command",
|
||||
"您輸入了錯誤的HEKY":"You entered the wrong HEKY",
|
||||
"您輸入了錯誤的TYPE":"You entered the wrong TYPE",
|
||||
"警告":"Warning",
|
||||
"您確定要新增值或是修改值嗎?":"Are you sure you want to add or modify a value?",
|
||||
"成功的創建或修改註冊表值":"Successfully created or modified registry value",
|
||||
"分析文件函數":"Analyze File Func",
|
||||
"分析文件哈希值":"Analyze File Hashes",
|
||||
"分析文件位元":"Analyze File Bits",
|
||||
'尋找結果:':'Find result:',
|
||||
'正在尋找: ':'Searching: ',
|
||||
'找到檔案: ':'File found: ',
|
||||
'未找到檔案':'File Not Found',
|
||||
'創建日期: ':'Created Date: ',
|
||||
"您確定要修改用戶密碼嗎?":"Are you sure you want to change the user password?",
|
||||
"IP查詢":"IP query",
|
||||
"您的ip地址為:{}":"Your ip address is: {}",
|
||||
"您確定要重置網路配置嗎?":"Are you sure you want to reset the network configuration?",
|
||||
"重置網路配置成功":"Reset network configuration successful",
|
||||
"設定":"Setting",
|
||||
"關於":"About",
|
||||
"結束進程":"End process",
|
||||
"啟用該選項可以實時監控進程中的惡意軟體並清除。":"Enable this option to monitor and remove malware in the system in real time.",
|
||||
"啟用該選項可以提高掃描靈敏度,但這也可能會造成誤殺。":"Enable this option can improve scanning sensitivity, but it can also cause manslaughter.",
|
||||
'成功攔截惡意軟體: ':'Malware blocking success: ',
|
||||
'成功修復註冊表: ':'Repair registry success: ',
|
||||
'成功修復引導扇區: PhysicalDrive0':'Repair boot sector success: PhysicalDrive0',
|
||||
'正在掃描檔案安全性: ':'Scanning file security: ',
|
||||
'惡意軟體攔截失敗: ':'Malware blocking failed: ',
|
||||
'修復系統權限':"Repair System Permissions",}
|
||||
@@ -0,0 +1,45 @@
|
||||
translations = {"zh_TW": {"已开启": "已開啟","已关闭": "已關閉","On": "已開啟","Off": "已關閉"},
|
||||
"zh_CN": {"On": "已开启","Off": "已关闭","已開啟": "已开启","已關閉": "已关闭",
|
||||
"嗎": "吗","項": "项","復": "复","攔": "拦","請": "请","掃描": "扫描",
|
||||
"鑰": "钥","統": "统","當": "当","確定": "确认","檔案": "文件",
|
||||
"權限": "权限","惡意": "恶意","設定": "设置","後": "后","發現": "发现",
|
||||
"關於": "关于","防護": "保护","軟體": "软件","引導扇區":"引导扇区",
|
||||
"錯誤": "错误","實時": "实时"},
|
||||
"en_US": {"Off":"Off","提示":"Tips","存取被拒":"Access denied","添加數據庫":"Add database",
|
||||
"個病毒":" Virus","正在掃描: ":"Scanning: ","掃描失敗。":"Scan failed.","已关闭":"Off","On":"On",
|
||||
"病毒掃描":"Virus scan","正在刪除: ":"Deleting: ","請選擇掃描方式":"Please select a scan method",
|
||||
"正在初始化中,請稍後...":"Initializing, please wait...","當前未發現惡意軟體。":"No malware currently found.",
|
||||
"這部裝置已受到保護":"This device has been protected","錯誤":"Error", "錯誤: ":"Error: ",
|
||||
"這部裝置目前不安全":"This device is currently unsafe","修復完成!":"Repair complete!",
|
||||
"當前已發現惡意軟體共{}項。":"A total of {} items of malware have been found so far.",
|
||||
"安全密鑰錯誤":"Security Key Error","完成":"Finish","修復系統檔案":"Repair System Files",
|
||||
"尚未啟用實時防護":"Real-time Protect is not enabled","修復失敗":"Repair failed",
|
||||
"請輸入需要尋找的檔案":"Please enter the file you want to find","清理失敗":"Cleanup failed",
|
||||
"成功: 已執行成功。":"Success: Executed successfully.","錯誤: 執行失敗。":"Error: Execution failed.",
|
||||
"您確定要修復系統權限嗎?":"Are you sure you want to fix system permissions?",
|
||||
"您確定要修復系統檔案嗎?":"Are you sure you want to repair the system files?",
|
||||
"清理系統檔案":"Clean up system files","清理完成":"Cleanup complete","刪除檔案":"Delete file",
|
||||
"您確定要清理系統檔案嗎?":"Are you sure you want to clean the system files?",
|
||||
"啟用安全模式":"Enable safe mode","啟用失敗":"Enable failed","禁用安全模式":"Disable safe mode",
|
||||
"您確定啟用安全模式嗎?":"Are you sure you enable safe mode?","禁用失敗":"Disable failed",
|
||||
"使用該選項後需要重啟,現在要重啟嗎?":"A reboot is required after using this option, do you want to reboot now?",
|
||||
"您確定禁用安全模式嗎?":"Are you sure you want to disable Safe Mode?","刪除失敗":"Failed to delete",
|
||||
"您確定刪除該檔案嗎?":"Are you sure you want to delete this file?","刪除成功":"Success to deleted",
|
||||
"運行成功":"Run successfully","不是有效命令":"Not a valid command","警告":"Warning",
|
||||
"您輸入了錯誤的HEKY":"You entered the wrong HEKY","分析文件函數":"Analyze File Func",
|
||||
"您輸入了錯誤的TYPE":"You entered the wrong TYPE","分析文件哈希值":"Analyze File Hashes",
|
||||
"您確定要新增值或是修改值嗎?":"Are you sure you want to add or modify a value?",
|
||||
"成功的創建或修改註冊表值":"Successfully created or modified registry value",
|
||||
"分析文件位元":"Analyze File Bits","尋找結果:":"Find result:","正在尋找: ":"Searching: ",
|
||||
"找到檔案: ":"File found: ","未找到檔案":"File Not Found","創建日期: ":"Created Date: ",
|
||||
"您確定要修改用戶密碼嗎?":"Are you sure you want to change the user password?",
|
||||
"IP查詢":"IP query","您的ip地址為:{}":"Your ip address is: {}","設定":"Setting",
|
||||
"您確定要重置網路配置嗎?":"Are you sure you want to reset the network configuration?",
|
||||
"重置網路配置成功":"Reset network configuration successful","關於":"About",
|
||||
"結束進程":"End process","成功攔截惡意軟體: ":"Malware blocking success: ",
|
||||
"啟用該選項可以實時監控進程中的惡意軟體並清除。":"Enable this option to monitor and remove malware in the system in real time.",
|
||||
"啟用該選項可以提高掃描靈敏度,但這也可能會造成誤殺。":"Enable this option can improve scanning sensitivity, but it can also cause manslaughter.",
|
||||
"成功修復註冊表: ":"Repair registry success: ","修復系統權限":"Repair System Permissions",
|
||||
"成功修復引導扇區: PhysicalDrive0":"Repair boot sector success: PhysicalDrive0",
|
||||
"正在掃描檔案安全性: ":"Scanning file security: ","惡意軟體攔截失敗: ":"Malware blocking failed: ",
|
||||
"實時防護已開啟":"Real-time protection is enabled","已開啟":"On", "已關閉":"Off","已开启":"On",}}
|
||||
+1
-1
@@ -11,7 +11,7 @@ class Ui_MainWindow(object):
|
||||
MainWindow.setFont(font)
|
||||
MainWindow.setFocusPolicy(QtCore.Qt.TabFocus)
|
||||
icon = QtGui.QIcon()
|
||||
icon.addPixmap(QtGui.QPixmap("Library/PYAS/Icon/ICON.bmp"), QtGui.QIcon.Normal, QtGui.QIcon.Off)
|
||||
icon.addPixmap(QtGui.QPixmap("Library/PYAS/Icon/ICON.ico"), QtGui.QIcon.Normal, QtGui.QIcon.Off)
|
||||
MainWindow.setWindowIcon(icon)
|
||||
MainWindow.setIconSize(QtCore.QSize(24, 24))
|
||||
MainWindow.setToolButtonStyle(QtCore.Qt.ToolButtonIconOnly)
|
||||
|
||||
@@ -1,7 +1,7 @@
|
||||
import pyinstaller_versionfile
|
||||
pyinstaller_versionfile.create_versionfile(
|
||||
output_file="versionfile.txt",
|
||||
version='2.6.2',
|
||||
version='2.6.5',
|
||||
company_name="PYAS Security",
|
||||
file_description="Python Antivirus Software",
|
||||
internal_name="PYAS",
|
||||
|
||||
@@ -1,5 +1,4 @@
|
||||
# PYAS (Python Antivirus Software)
|
||||
PYAS is not only free and open source without ads,Also uses multiple intelligent protection engines,Always protect the privacy and data security of users.
|
||||
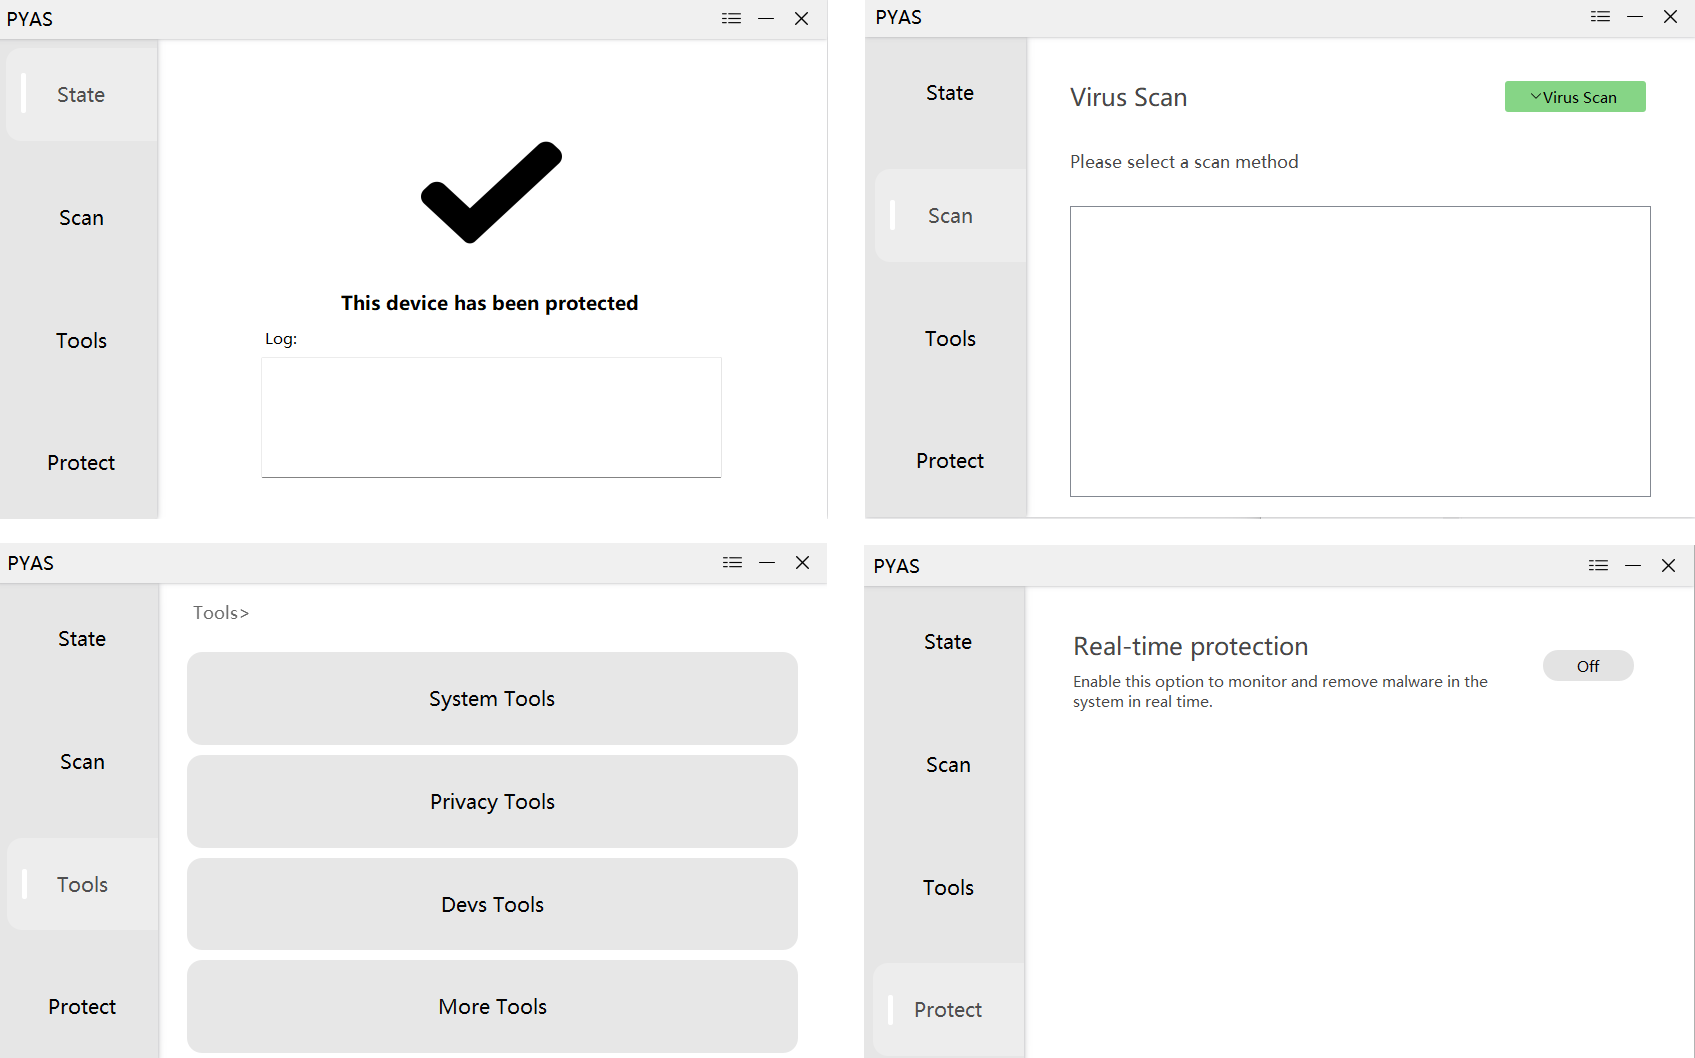
|
||||
|
||||
|
||||
@@ -7,9 +6,6 @@ PYAS is not only free and open source without ads,Also uses multiple intelligent
|
||||
https://pyantivirus.wixsite.com/pyas ,
|
||||
https://github.com/87owo/PYAS
|
||||
|
||||
## Hashes Library
|
||||
https://virusshare.com/hashes
|
||||
|
||||
## MIT License
|
||||
https://github.com/87owo/PYAS/blob/main/LICENSE.md
|
||||
|
||||
@@ -17,7 +13,7 @@ https://github.com/87owo/PYAS/blob/main/LICENSE.md
|
||||
Windows 8.1, 10, 11 (64-bit), Ram 1GB, Rom 1GB or higher
|
||||
|
||||
## Import Module
|
||||
os, sys, time, json, psutil, struct, win32api, win32con, requests, socket, platform, cryptocode, subprocess, pefile, hashlib, PYAS_English, win10toast, threading, random, PyQt5, PYAS_UI
|
||||
os, sys, time, json, psutil, struct, win32api, win32con, requests, socket, platform, cryptocode, subprocess, pefile, hashlib, PYAS_Language, threading, random, PyQt5, PYAS_UI
|
||||
|
||||
## Special Thanks
|
||||
Wix, VirusShare, mtkiao129, LenStevens
|
||||
|
||||
Reference in new issue
Block a user